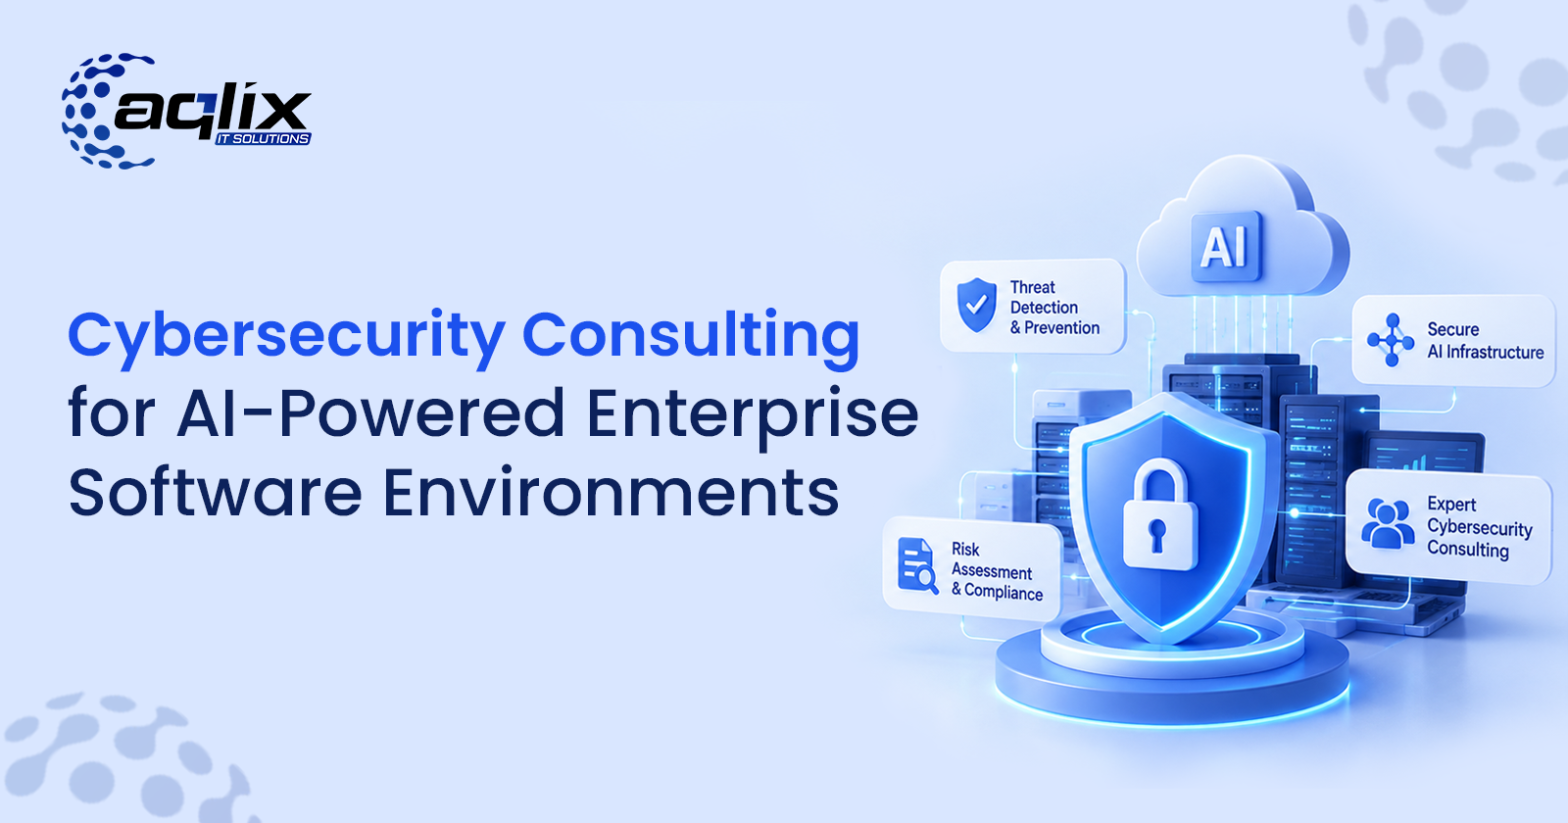

Every business is adopting AI, customer service AI chatbots, and reporting AI dashboards. Most enterprise AI deployments happened very quickly and without thought. Every new AI tool is a new connection into enterprise systems, and not every company knows who or what can access their systems after they set up a new AI tool.
At Aqlix IT Solutions, we see companies quickly adding AI features to products before their security can keep up. The missing security controls remain hidden until there is a major issue. Hiring cybersecurity consultants early in the product development lifecycle ensures that these gaps are identified and closed to prevent attackers from exploiting them.
Why AI-Powered Systems Need a Different Security Approach
Traditional security checklists weren’t built with AI in mind, and that gap shows the moment a business plugs machine learning models into core enterprise systems. Solid AI & machine learning security practices have to account for model tampering, data poisoning, and unpredictable outputs, none of which fit neatly into the vulnerability scans and firewalls most legacy security programs still rely on.
1. Expanded Attack Surfaces from AI Integrations
An AI chatbot or recommendation engine on a new enterprise platform creates APIs, data connections, and attack surfaces never before present. Hackers have learned to chiefly attack these newer features, as they are less heavily protected and monitored.
Application modernization efforts can solve some of these security problems. Rebuilding legacy applications can limit the number of older attack vectors that have been left open by AI integrations. This means attackers will have to work harder to successfully hack the enterprise system and have fewer paths to do so.
2. Data Privacy Risks in AI Pipelines
Trust in AI models is premised on trust in the data used to build those models. Data used for AI model building may include sensitive customer information, financial data, and company data that moves through different systems. Every instance where data is collected, stored, or processed is a leak. Many organizations underestimate how many leaks they have.
Custom software development for AI pipelines will include security and data minimization by default. Off-the-shelf AI systems often include extensive data collection that is hidden to the user. Purpose-built systems can control the data provided to AI models, unlike off-the-shelf solutions.
Building a Security-First AI Strategy
It is better to plan security features of AI systems at the onset of a digital transformation rather than at the end. Security reviews of the AI process at each step, from data collection to the deployment of models, help users find breakdowns in the security process in the early stages, rather than after the fact. This ensures the security of the process.
1. Continuous Testing and Vulnerability Assessment
Due to features being added, model updates, and changes to training data, AI systems frequently go through updates that render security audits invalid within a short time of being conducted. The systems adapt to address launch-time vulnerabilities; however, new, unknown vulnerabilities come into existence that were possibly left open after the initial approval of the system.
Vulnerabilities discovered by gaps in software increase the risk to your organization. Performing regular penetration testing and automated vulnerability scans throughout regular software QA testing & automation cycles can expose these gaps before attackers do. By building testing processes throughout each release, AI systems remain resilient to the threats posed by the rapid growth and adaptability of enterprise systems.
2. Secure Cloud Infrastructure for AI Workloads
Most AI workloads run on cloud infrastructure by default, which means the security of the underlying platform matters as much as the AI model running on top of it. Misconfigured storage buckets, overly broad permissions, and exposed APIs are some of the most common ways enterprise AI systems get breached.
Securing cloud applications properly means enforcing least-privilege access, encrypting data both in transit and at rest, and continuously monitoring for unusual activity across every connected service. For AI-powered environments, this means securing the model endpoints too, since a protected API matters more than typical enterprise software alone can ever offer.
Conclusion
Cybersecurity can’t be an afterthought once AI runs operations, because the consequences will be far greater if a breach occurs. This is where Aqlix IT Solutions comes in. They work with businesses to develop security at each stage of AI development, from the early development stages up until the system is monitored and maintained after launch.
It is critical that you test the security of your AI systems before a breach occurs. Aqlix IT Solutions will evaluate your current AI systems and answer any questions you might have. Prevent the breaches from causing headaches for you and your customers by calling them now.
FAQs
Why do AI-powered enterprise systems need specialized cybersecurity consulting?
Most traditional security tools cannot address risks related to model manipulation, data poisoning, and AI-related APIs. To protect against these unique AI risks, specialized consulting will provide an early detection of those risks. Security architecture will need to account for how machine learning models will behave in the future, as opposed to just another software product located within the enterprise stack.
What are the biggest security risks in AI-powered enterprise environments?
The most significant threats are leaks of data via AI pipelines, exposed or insecure model APIs, over-granted access integrations, and generation of adversarial attack models to alter output. Threats are hard to spot because they bypass the traditional security tests. Monitoring of AI security continuously is much more important than it has ever been.
How is securing an AI system different from securing regular enterprise software?
Regular software has inputs and outputs that are predictable and unchanging, but changes to these inputs or even slight changes in how AI models are used may have dramatic, unpredictable results. As such, a model written years ago may be secure and functional when introduced, only to become a threat several years later. Protecting AI models must therefore take a surveillance approach to understand the model’s behavior over time.
How long does an AI security assessment usually take?
Most assessments take four to eight weeks to complete and depend on the number of AI integrations, data sources, and existing systems. The more mature the security practices, the quicker the assessment takes. The very large enterprises with multiple AI deployments across departments require multiple assessments instead of a single assessment covering all domains.
Should smaller businesses worry about AI security too?
Yes, since smaller businesses first adopt AI tools without the company’s security teams reviewing them. Aqlix IT Solutions is a solid partnership for smaller companies who can’t afford to build an AI security team. The smaller companies gain access to the same level of AI security that larger companies have.